scan: cloud · on-prem · CI/CD · third-party0 at risk
Your cryptographic estate is bigger than you think, scattered across cloud, on-prem, CI/CD, and third parties, with no single owner and no central record. Get the map before you commit to a fix.
scan: cloud · on-prem · CI/CD · third-party0 at risk
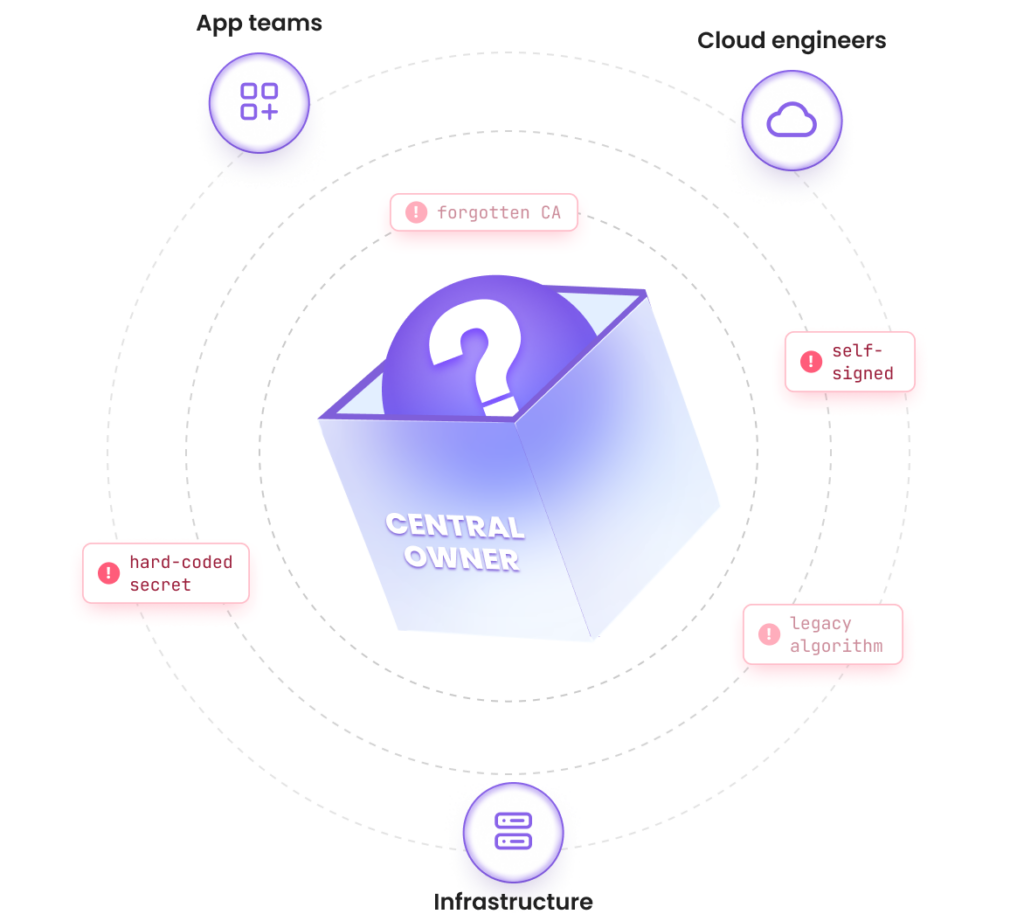
Cryptography: Deployed by Everyone, Owned by No One.
App teams, cloud engineers, and infrastructure groups each issue and manage their own keys and certificates. Spreadsheets go stale the day they’re finished, and they miss exactly what causes outages: self-signed certs, forgotten internal CAs, hard-coded secrets, legacy algorithms buried in old applications.
0%
name poor cryptographic visibility their top readiness barrier
0%
are actively preparing for post-quantum
Ponemon Institute, sponsored by Entrust, 2026
Discovery isn't a preliminary step. It's what determines whether the real project gets scoped right.
Every Domain, Every
Environment: Encompassed.
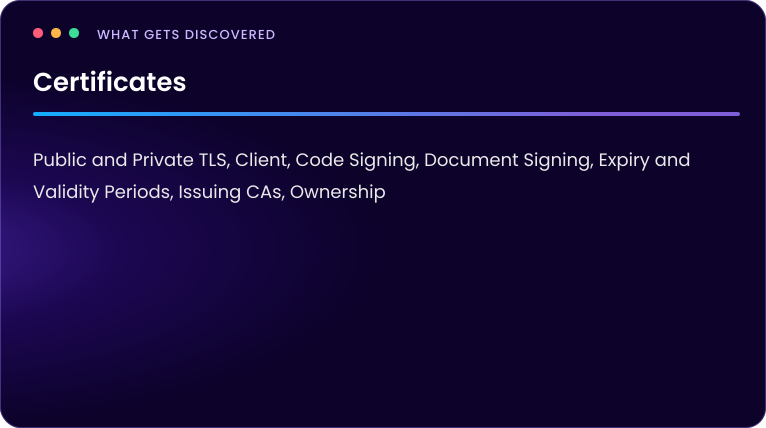
Certificates
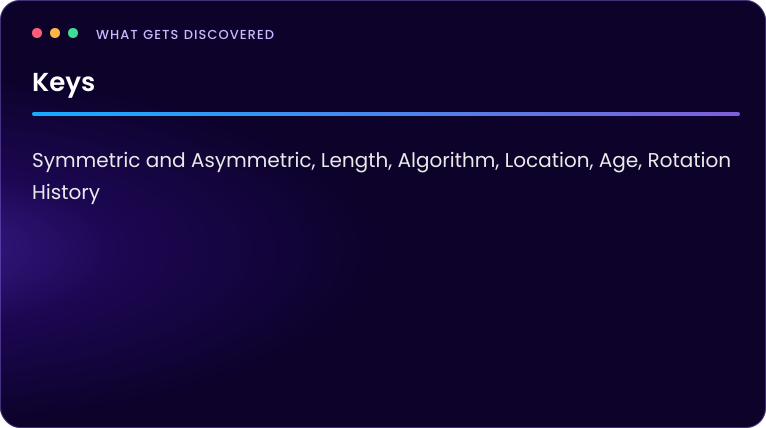
Keys
Secrets
PKI
Crypto Libraries
Infrastructure
Certificates
Keys
Secrets
PKI
Crypto Libraries
Infrastructure
On-prem, multi-cloud, hybrid, third-party managed, all in scope. A partial inventory just means a false sense of readiness.
Four Clocks Running at Once
Quantum Readiness
Harvest-now-decrypt-later risk today, plus a forced migration off RSA and ECC ahead. The assessment shows which assets are quantum-vulnerable, which protect your most sensitive data, and where you're locked into algorithms you can't swap without a rebuild.
47-Day Certificate Readiness
TLS lifetimes are shrinking in stages, down to 47 days. The assessment shows your renewal method per asset, how many still need a human, and your real renewal volume once 47 days hits, usually the number that changes the internal conversation.
Compliance Deadlines (US & Canada)
Federal, national security, and sector mandates, all converging on 2027–2035. The assessment shows which mandates apply to you, which systems fall in scope, and whether your timeline holds up.
Audit & Governance Readiness
Proving your posture on demand, not reconstructing it during an audit. The assessment shows policy gaps, exceptions, and where no one owns the record.
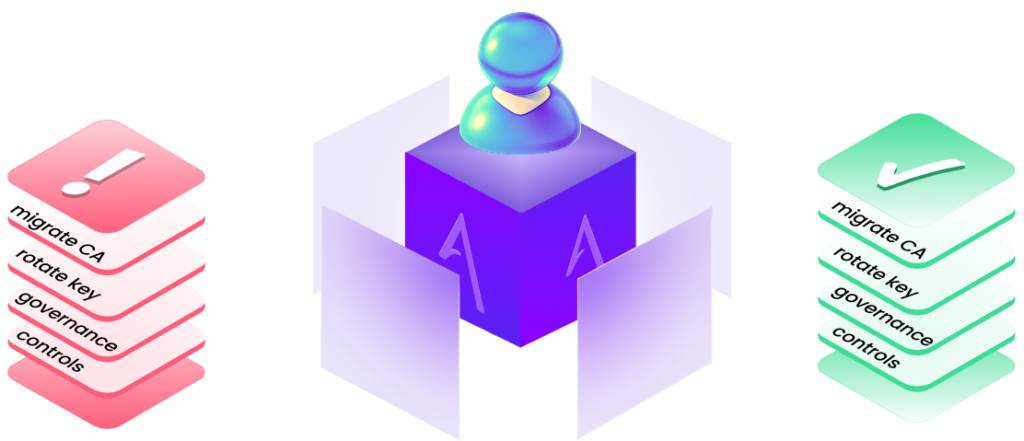
An assessment tells you what's wrong and in what order. Remediation is where that roadmap becomes actual work: migrating certificate authorities, rotating exposed keys, replacing weak algorithms, standing up the migrating certificate authorities that keep the same gaps from reappearing. This isn't handed to your team as homework. Accutive's engineers execute it.
A Finding Isn't a Fix. Automation Is.
Discovery uncovers the problem. Automation is what stops it from coming back in six months.
Continuous Discovery
Your inventory stays current, not just accurate the day it was built.
Lifecycle Automation
Issuance, renewal, revocation, and rotation, no ticket required.
Policy Enforcement
Non-compliant assets get flagged or blocked at issuance, not after.
Compliance reporting stops being a quarterly scramble. It becomes a byproduct of how the system already runs.
The assessment tells you what to fix, and in what order. Next: what you run it on.
One Platform. Every Layer of Cryptographic Control.
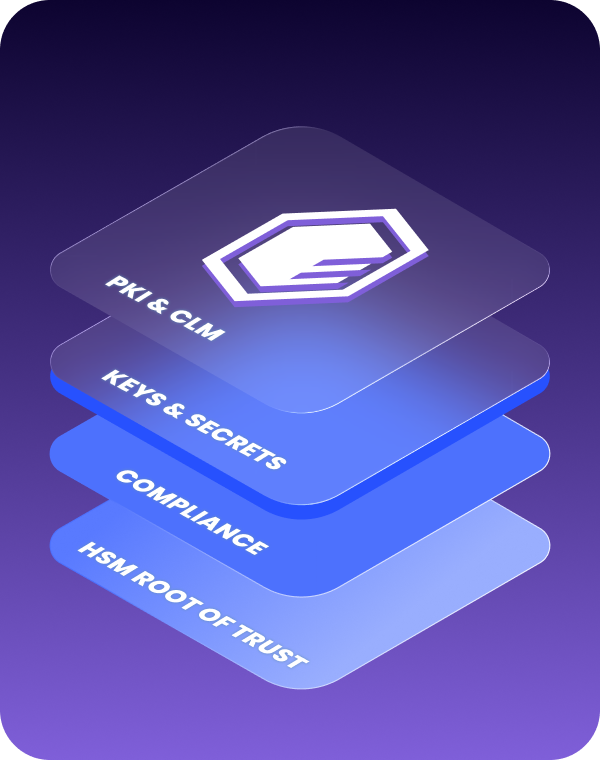
Entrust unifies PKI, certificate lifecycle management, key and secrets management, and HSMs into a single system.
Centralized Control PKI, HSMs, and crypto lifecycle in one platform, less sprawl.
Automated Lifecycle & Policy Discovery, renewal, and enforcement, without a manual step.
Reduced Operational Risk Catch expiring or misconfigured assets before an outage hits.
Post-Quantum Readiness Crypto-agility built in, ready for the algorithm transition.
Governance & Audit Confidence Prove your posture on demand, not after the fact, always.
Interoperability at Scale Connects into the identity and IT stack you already run.
What's Inside
PKI & Certificate Lifecycle Management
Agentless File-Level Data Encryption
HSM Manager for Distributed nShield Estates
Certificate Manager for Enterprise Certificate Visibility and Automation
Compliance Manager for Policy Control
Key & Secrets Lifecycle Management
FIPS 140-3 HSM Root of Trust, On-Prem or Cloud
2009
Founded · North America
Why Accutive Security
Founded in 2009, Accutive Security has completed hundreds of PKI implementations for some of North America's most impactful organizations. As a certified Entrust partner, we go beyond reselling, with active delivery relationships across advisory, implementation, integration, and migration for nShield HSM environments specifically. Every assessment runs through our Innovation Lab, so issues get caught and resolved before they ever reach your environment.